
PQC exposure analyser: harvest now, decrypt later
Point it at a pcap or a live tap and it reads each TLS handshake to flag the traffic a future quantum computer could decrypt from a recording made today. A concrete list of services and volumes, not an abstract panic.
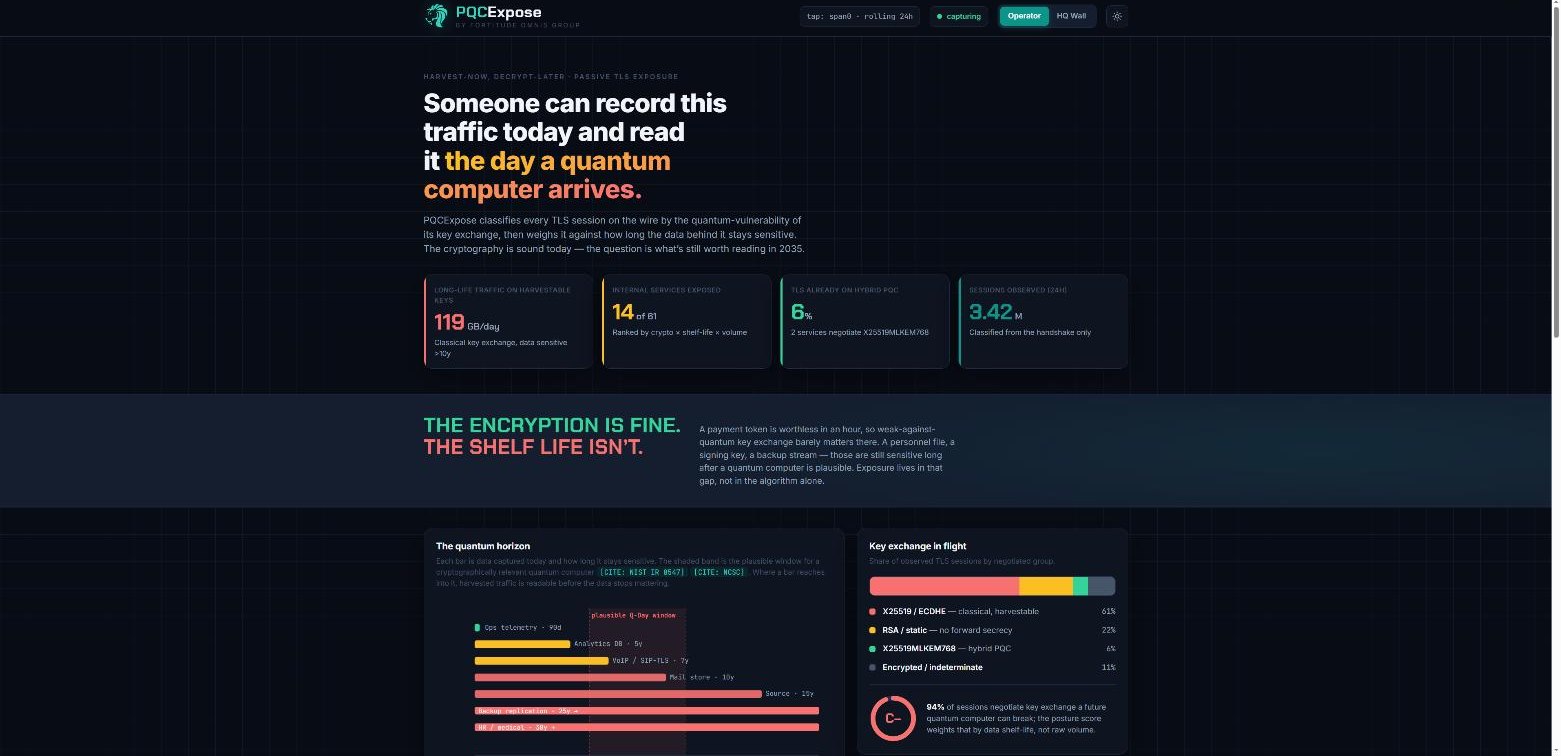
Most of the noise about quantum computers and cryptography is either breathless or bored, and both reactions skip straight past the one version of the threat that's genuinely worth acting on today. It isn't that someone breaks your TLS tomorrow. It's harvest now, decrypt later: someone records your encrypted traffic today, sits on it, and decrypts it in ten or fifteen years when the hardware catches up. If the data still matters by then, you've already lost it. You just don't know it yet.
So it measures your exposure to exactly that. Point it at a packet capture or a live tap and it reads each TLS session's key exchange and certificate chain, then classifies how much of your traffic is vulnerable in the harvest-now sense. The output isn't a lecture. It's an inventory: these fourteen internal services, this much traffic a day, negotiating key exchanges a recording made now could unpick later.
The hard part
The hard part is honesty in both directions. Modern TLS hides almost all of its content, so you're classifying from the handshake, which means being precise about what the handshake actually tells you and what it doesn't. And the risk has to be presented without the fearmongering that made most people tune this subject out in the first place. A service is only a problem if the data it carries is still sensitive on the timescale the migration actually runs to, and the standards bodies have already put real dates on that. Plenty of data has a shelf life longer than the runway.
tls sessions (24h tap)
  payments-api   TLS1.3  X25519            harvest-now exposed    4.1 GB/day
  internal-bus   TLS1.2  ECDHE-secp256r1   harvest-now exposed    0.9 GB/day
  vault          TLS1.3  X25519MLKEM768    pqc-hybrid, safe       0.3 GB/day
THE ENCRYPTION IS FINE. THE SHELF LIFE ISN'T.
It's in build now, and the first working version already does the core job. It sits on a tap, classifies every session from its handshake, and lays the results out as an inventory rather than an alarm: traffic by service, key exchange by share, and a shelf-life view that sets a plausible quantum horizon against how long each stream's data stays sensitive. The posture score weights that shelf-life ahead of raw volume, because a gigabyte of payment tokens that die in an hour matters far less than a slow drip of personnel files. What's left is the less glamorous half: hardening the classifier against the long tail of key exchanges, and getting the shelf-life question in front of the person who can actually answer it, because the tool's job is to turn "we should think about post-quantum at some point" into a list someone can work down. It reads the same threat as the post-quantum scanner in OSPulse, from the other end of the wire. Not what your code ships, but what your network's already leaking onto tape.